


About this integration
Call any API or web service, even one without a native app. Send requests and download files, with your choice of authentication. Use it from the workflow canvas with no custom glue script required.
This integration exposes 0 triggers, 0 search modules and 2 actions as workflow nodes. Authentication uses basic or basic or basic or basic or basic or basic or basic or oauth or oauth authentication.
This is a focused integration — 2 public modules. The field tables below are the full reference. Connecting it uses Header / Parameter Name, Key Value, and Send In.
How to connect
The credential form asks for Header / Parameter Name, Key Value, Send In, and Access Key ID.
Prefer the interactive builder form? Open it on the app page.
Enter your credentials below. WEXTL stores them encrypted and uses them only to call the API on your behalf.
| Field | Type | Help |
|---|---|---|
Header / Parameter NameRequired | text | The name of the header or query parameter, e.g. X-API-Key or api_key |
Key ValueRequired | password | The API key value. Stored encrypted. |
Send InRequired | select | — |
Enter your credentials below. WEXTL stores them encrypted and uses them only to call the API on your behalf.
| Field | Type | Help |
|---|---|---|
Access Key IDRequired | text | — |
Secret Access KeyRequired | password | Stored encrypted. |
RegionRequired | text | e.g. us-east-1 |
ServiceRequired | text | e.g. execute-api, s3 |
Session Token | password | Optional — for temporary STS credentials |
Enter your credentials below. WEXTL stores them encrypted and uses them only to call the API on your behalf.
| Field | Type | Help |
|---|---|---|
UsernameRequired | text | — |
PasswordRequired | password | Stored encrypted. |
Enter your credentials below. WEXTL stores them encrypted and uses them only to call the API on your behalf.
| Field | Type | Help |
|---|---|---|
TokenRequired | password | The bearer token to send in the Authorization header. Stored encrypted. |
Enter your credentials below. WEXTL stores them encrypted and uses them only to call the API on your behalf.
| Field | Type | Help |
|---|---|---|
UsernameRequired | text | — |
PasswordRequired | password | Stored encrypted. |
Enter your credentials below. WEXTL stores them encrypted and uses them only to call the API on your behalf.
| Field | Type | Help |
|---|---|---|
SecretRequired | password | Stored encrypted. |
Algorithm | select | — |
Signature Encoding | select | — |
Signature HeaderRequired | text | The response header name the computed signature is sent in, e.g. X-Signature. |
Signature Prefix | text | Optional prefix, e.g. sha256= |
Timestamp Header | text | Optional — when set, a unix-seconds timestamp is signed and sent in this header, e.g. X-Timestamp |
Enter your credentials below. WEXTL stores them encrypted and uses them only to call the API on your behalf.
| Field | Type | Help |
|---|---|---|
Client CertificateRequired | textarea | Client certificate (PEM) |
Client Private KeyRequired | textarea | Client private key (PEM) |
Private Key Passphrase | password | Optional — only needed if the private key above is encrypted. Stored encrypted. |
CA Certificate | textarea | Optional — pin the server CA (PEM) |
You’ll be redirected to sign in and approve access — your password is never shared with WEXTL.
| Field | Type | Help |
|---|---|---|
Authorization URLRequired | url | The OAuth 2.0 authorization endpoint URL (e.g. https://auth.example.com/oauth/authorize). Must be a public HTTPS URL — internal/private addresses are rejected. |
Token URLRequired | url | The OAuth 2.0 token endpoint URL (e.g. https://auth.example.com/oauth/token). Must be a public HTTPS URL — internal/private addresses are rejected. |
Client IDRequired | text | The OAuth 2.0 client ID issued by the authorization server. |
Client SecretRequired | password | The OAuth 2.0 client secret issued by the authorization server. Stored encrypted — never exposed in blueprints or logs. |
Token Endpoint Auth | select | How to send the client ID and secret to the token endpoint. 'Client Secret Post' puts them in the request body (default, most compatible). 'Client Secret Basic' sends them as an HTTP Basic Authorization header instead. |
Scopes | text | Space- or comma-separated list of OAuth 2.0 scopes to request (e.g. read write or openid profile). Optional — leave blank if the server grants a default scope. |
Audience | text | Optional audience parameter sent in the token request (used by some providers such as Auth0). |
Prompt | select | Controls whether the authorization server prompts the user for reauthentication or consent. 'consent' forces the consent screen (required by Google to receive a refresh_token with offline access). 'select_account' lets the user pick which account to use. |
Access Type | select | Google-specific: set to 'offline' to receive a refresh_token that allows renewing access without user interaction. Requires prompt=consent on the first authorization. Leave as 'Default' for providers that do not use this parameter. |
Extra Authorization Parameters | array | Additional query parameters to append to the authorization URL. Use this for provider-specific parameters not covered by the fields above (e.g. hd=example.com for Google Workspace domain hint). |
Extra Token Body Parameters | array | Additional key/value parameters to include in the token-exchange request BODY (urlencoded). Use for provider-specific fields not covered above (e.g. a resource or tenant parameter). Sent when exchanging the authorization code for tokens. |
Extra Token Query Parameters | array | Additional key/value query-string parameters appended to the token-exchange request URL. Rare, but some providers require params in the query string rather than the body. |
Extra Refresh Body Parameters | array | Additional key/value parameters to include in the token REFRESH request BODY (urlencoded). Sent each time the access token is renewed. |
Extra Refresh Query Parameters | array | Additional key/value query-string parameters appended to the token REFRESH request URL. |
You’ll be redirected to sign in and approve access — your password is never shared with WEXTL.
| Field | Type | Help |
|---|---|---|
Token URLRequired | url | The OAuth 2.0 token endpoint URL (e.g. https://auth.example.com/oauth/token). Must be a public HTTPS URL — internal/private addresses are rejected. |
Client IDRequired | text | The OAuth 2.0 client ID issued by the authorization server. |
Client SecretRequired | password | The OAuth 2.0 client secret issued by the authorization server. Stored encrypted — never exposed in blueprints or logs. |
Scopes | text | Space- or comma-separated list of OAuth 2.0 scopes to request (e.g. read write). Optional — leave blank if the server grants a default scope. |
Audience | text | Optional audience parameter sent in the token request (used by some providers such as Auth0). |
Token Endpoint Auth | select | How to send the client ID and secret to the token endpoint. 'Client Secret Post' puts them in the request body (default, most compatible). 'Client Secret Basic' sends them as an HTTP Basic Authorization header instead. |
Use it in workflow automation
Add Download a File as a workflow step.
The canvas below shows the integration — watch the video, then drop a node onto the canvas.
Start with the Download a File step and run it on demand or on a schedule.
Then add Send a Request as the next node. Branch, filter, or hand off to other integrations from there.
The integration includes 2 ready-made modules for developer tools work — each run logs its inputs and outputs for debugging.
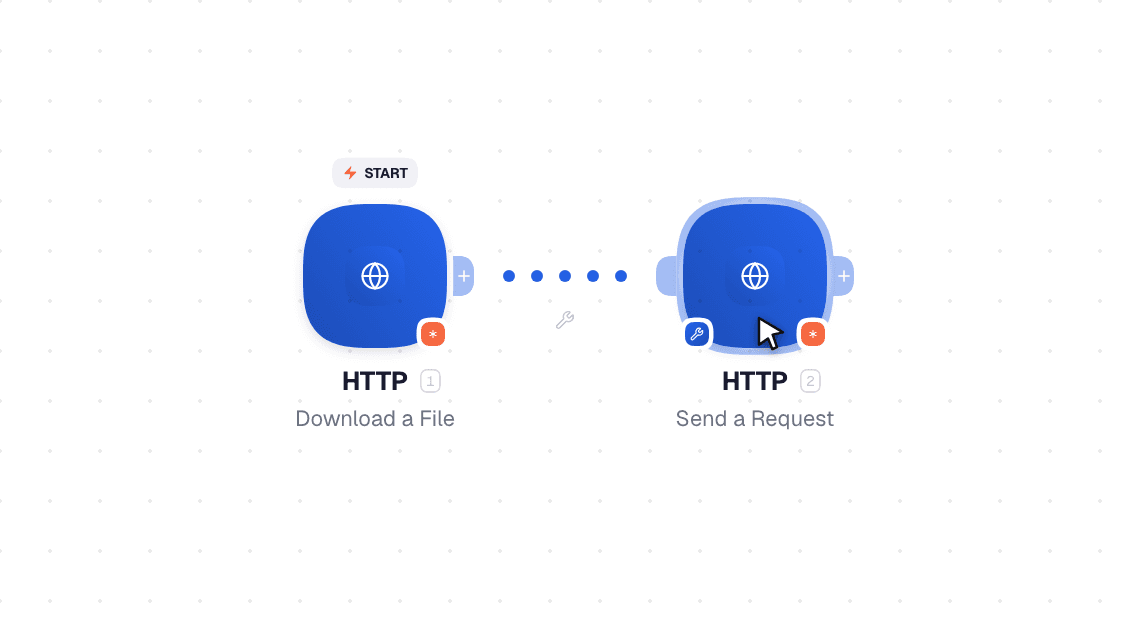
HTTP workflow on the canvas: Download a File then Send a Request
Triggers, searches and actions
Use the tables below to inspect HTTP's 0 triggers, 0 search modules, and 2 actions.
Actions
2 action modules cover the full range of create, update, and delete operations.
- Download a File
- Send a Request
Explore the fields available for each HTTP trigger, search, and action.
Actions
| Field | Type |
|---|---|
MethodRequired | choice |
URLRequired | url |
Headers | array |
Header | object |
Filename | text |
Max File Size (bytes) | number |
Proxy | object |
Proxy URL | text |
Proxy Username | text |
Proxy Password | secret |
| Field | Type |
|---|---|
File Data | text |
Filename | text |
File Size (bytes) | number |
Content Type | text |
Response Headers | object |
Status Code | number |
| Field | Type |
|---|---|
MethodRequired | choice |
URLRequired | url |
Headers | array |
Header | object |
Query Parameters | array |
Parameter | object |
Body Type | choice |
Pagination | choice |
Split Response into Separate Bundles | boolean |
Response Format | choice |
Timeout (ms) | number |
Ignore SSL/TLS Certificate Errors | boolean |
Proxy | object |
Proxy URL | text |
Proxy Username | text |
Proxy Password | secret |
| Field | Type |
|---|---|
Body | text |
Response Headers | object |
Status Code | number |